Currently SOC & Security Engineer @ Ansen Technologies

I build SOCs that detect what matters.

//SOC & Security Engineer

Security engineer working across Microsoft Sentinel, Defender XDR and Entra ID — building detection, telemetry pipelines and threat-hunting capability for enterprise and government clients. Delivered a full government SOC with zero post-deployment rework.

Abu Dhabi, UAE SC-200 · Security+ · CPT github.com/sherifrahim
sherif.rahim · latest roles
Sherif RahimSOC & Security Engineer · Abu Dhabi
Now at Ansen
  1. SOC & Security EngineerAnsen Technologies · Abu Dhabi
  2. IT Security & Support EngineerVirtual Team IT · Abu Dhabi
  3. Cybersecurity Engineer InternEhackify · pen testing & SOC
  4. IT Support CS AgentSutherland Global Services · Amazon
Full experience
SC-200Security+SC-900CPTSC-500 · in progress
0days

Critical infrastructure onboarded against a 10-day scope

0–0%

Monthly log-ingestion reduction across client tenants, detection coverage intact

0

Post-deployment rework on a full government SOC build

0+2

Certifications earned, with SC-500 and SC-401 in progress

What I do — a four-shot reel

Rec00:00:00:00Shot 01 / 04
Shot 01 · Detection

Detect.

KQL analytics rules, hunting queries and dashboards tuned against real identity, endpoint and cloud attack scenarios — higher alert fidelity, fewer false positives for the analysts who live in the queue.

Shot 02 · Telemetry

Connect.

End-to-end telemetry pipelines through Azure Monitor Agent, DCRs and native connectors — then continuous checks on connector health and data quality so monitoring never silently breaks.

Shot 03 · Hunting

Hunt.

Proactive threat hunting and threat intelligence — IOC validation, malware analysis and vulnerability assessment, mapped to MITRE ATT&CK and feeding straight into incident response and containment.

Shot 04 · Optimise

Tune.

Filtering low-value events and tuning data connectors to cut spend — without giving up detection coverage. Security that scales across multi-client SLAs and stays affordable to run.

01 — About

Attacker-aware, analyst-first.

I'm a Security Engineer who builds and operates enterprise and government SOC environments. My core is the Microsoft security stack — Sentinel, Defender XDR and Entra ID — across Azure and hybrid estates.

I like the engineering half of security: onboarding log sources properly, writing KQL that holds up in production, and tuning noise out of the pipeline so analysts spend their time on the alerts that matter.

My background in penetration testing and SOC internships gives me the attacker's view of the same environment — which is what makes a detection actually useful.

Based in Abu Dhabi, United Arab Emirates
Multi-client SOC delivery under SLAs
B.Tech Computer Science & Engineering, KTU

Detection engineering

KQL analytics rules, hunting queries and Sigma content tuned for fidelity, not volume.

SIEM & telemetry

Log-source onboarding, AMA/DCR pipelines, connector health and ingestion-cost control.

Hunting & intel

Hypothesis-led hunts, IOC validation and ATT&CK mapping that feed incident response.

Identity & posture

Entra ID, PIM, Defender for Endpoint/Cloud and Purview DLP administration and review.

02 — Experience

Where I've shipped.

From SOC internships to building production SOCs for government clients.

Scene 01 · Now

SOC and Security Engineer

Jun 2025 – Present

Ansen Technologies (formerly Anxinsec) · Abu Dhabi, UAE

  • Built and deployed production SOC environments for enterprise and government clients on Microsoft Sentinel — delivering a full government SOC with zero post-deployment rework and onboarding critical infrastructure in 4 days against a 10-day scope.
  • Engineered end-to-end telemetry pipelines for identity, endpoint, cloud and network logs using Azure Monitor, Log Analytics, AMA, Data Collection Rules and native connectors.
  • Developed and tuned KQL analytics rules, hunting queries, dashboards and Sentinel Analytics, improving alert fidelity while cutting false positives.
  • Optimised SIEM performance by filtering low-value events and tuning connectors — reducing monthly ingestion 30–40% across client tenants without hurting detection coverage.
  • Administered and secured Defender XDR, Defender for Endpoint, Entra ID, Purview DLP and Azure security services.
  • Performed proactive threat hunting and threat intelligence — IOC validation, malware analysis and vulnerability assessment using the MITRE ATT&CK framework, supporting incident response and containment.
  • Reviewed privileged access via Privileged Identity Management (PIM) to enforce controlled, auditable administrative access.
  • Investigated alerts and reviewed posture across Defender for Endpoint, Defender for Cloud and PIM.
  • Validated telemetry ingestion, connector health and data quality across multiple client environments.
  • Authored SOC engineering documentation, detection playbooks, onboarding procedures and runbooks.
Microsoft SentinelKQLDefender XDREntra IDAMA / DCRPurview DLPMITRE ATT&CK
Scene 02

IT Security and Support Engineer

Jan 2025 – Jun 2025

Virtual Team Information Technology · Abu Dhabi, UAE

  • Ran vulnerability assessments with Nessus, Defender XDR, WithSecure and Qualys across client environments, remediating findings and raising security posture.
  • Managed Linux and Windows servers, Active Directory, Microsoft 365, VPNs and endpoint protection while keeping uptime consistent.
  • Introduced workflow improvements across hardware, OS and network support that reduced average ticket resolution time.
Scene 03

IT Support CS Agent

Sep 2023 – Sep 2024

Sutherland Global Services (Amazon) · Kochi, India

  • Administered Microsoft 365 and Active Directory, enforcing account policies, access controls and secure configurations across a large user base.
  • Troubleshot and hardened network and endpoint environments with Cisco tooling, meeting SLA targets through JIRA and ServiceNow.
Scene 04

Cybersecurity Engineer Intern (part-time)

Jan 2024 – Sep 2024

Ehackify Cybersecurity · Kochi, India

Penetration Testing Intern — Jan to Mar 2024

  • Conducted penetration tests and vulnerability assessments with Nmap, Burp Suite, Metasploit, OpenVAS and ZAP, aligned to the OWASP Top 10.

SOC Intern — Apr to Jun 2024

  • Hands-on with SIEM environments across Splunk, Wazuh and Microsoft Sentinel for detection engineering, log correlation and alert triage.
  • Supported SOC workflows and IR processes within NIST SP 800-61 and ISO 27001 frameworks.
Scene 05 · Opening shot

SOC Intern

Jan 2023 – Jul 2023

CFSS Cyber Forensics Solutions · Kochi, India

  • Supported incident response and threat detection workflows using SIEM tooling across SOC monitoring operations.
  • Conducted vulnerability assessments and malware analysis, assisting with incident containment and investigation.
03 — How I build

Principles I build by.

Six habits that show up in my day job and my side projects alike — each one with the receipts.

Principle 01

Show your reasoning

A verdict nobody can audit is just an opinion. Whatever I build should be able to explain why it decided what it did.

The testCould a reviewer see why it decided that?
IN PRACTICE
Where I've done it

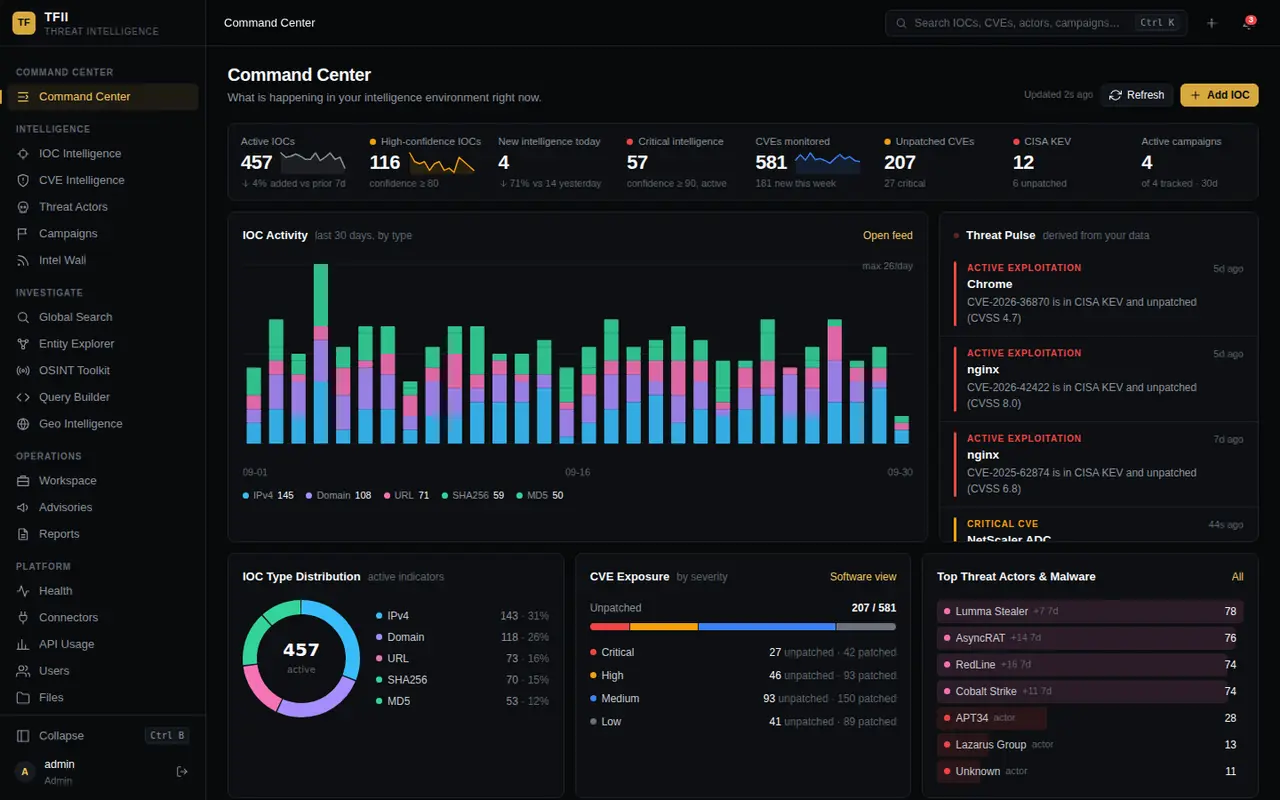
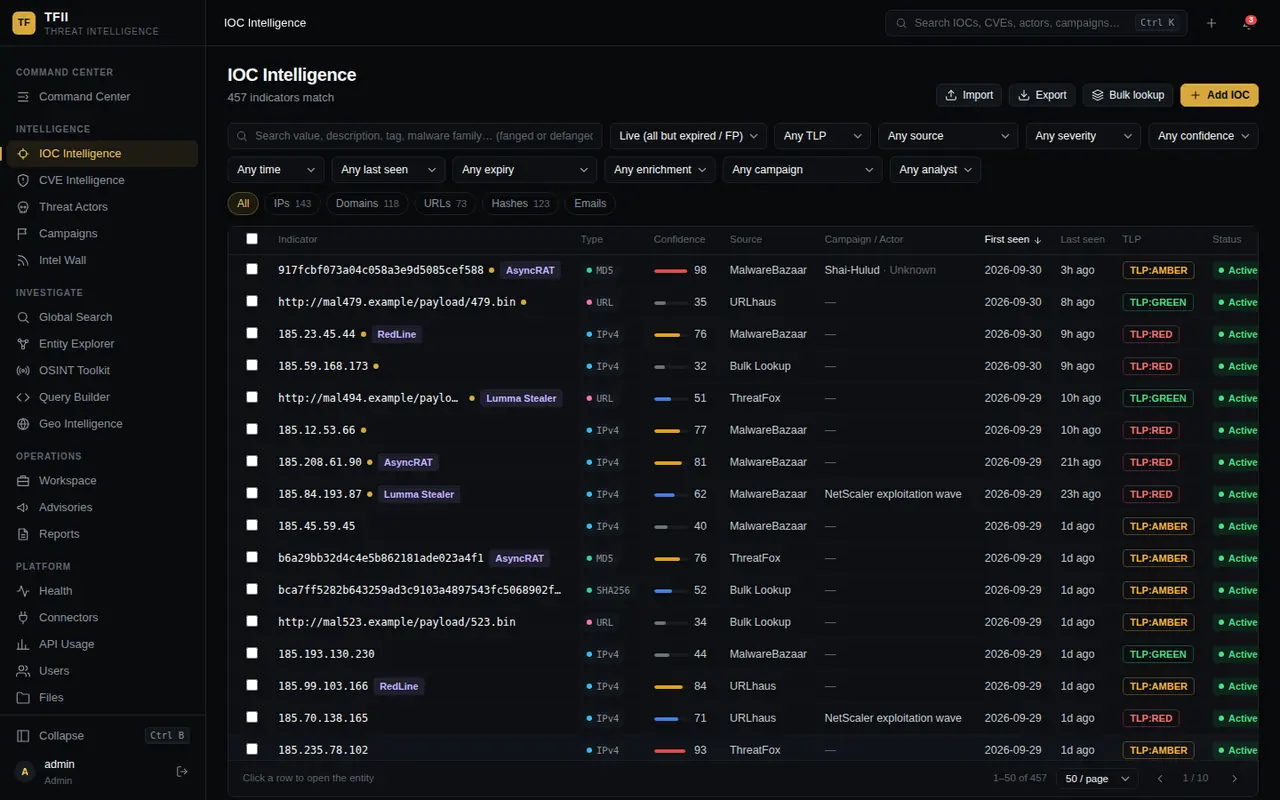
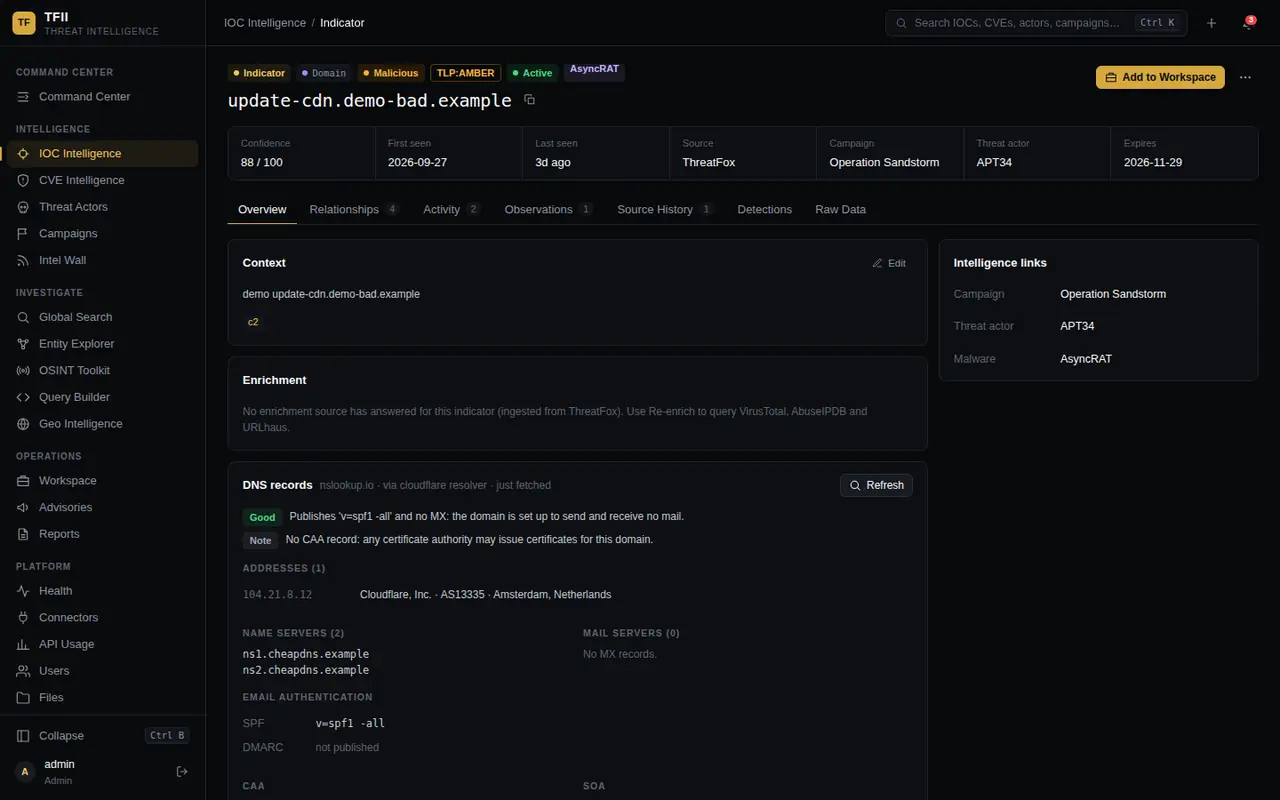
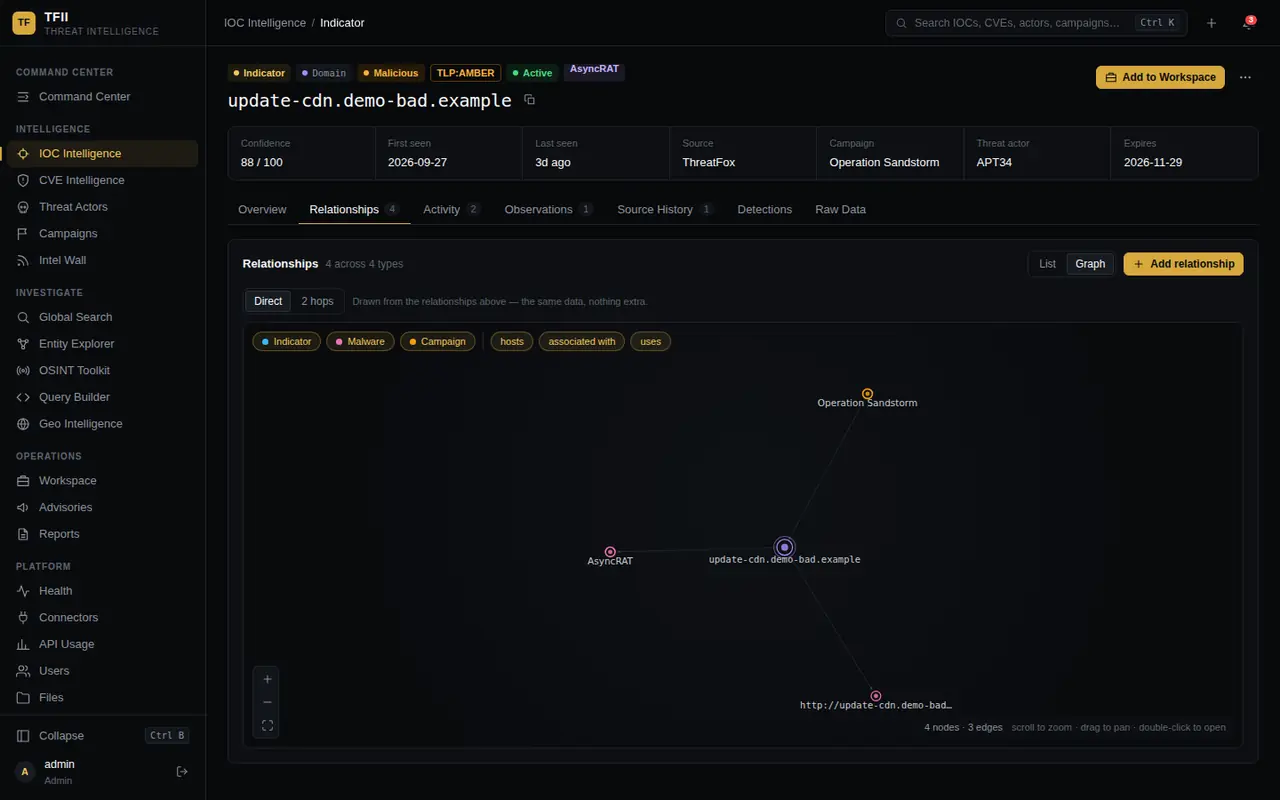
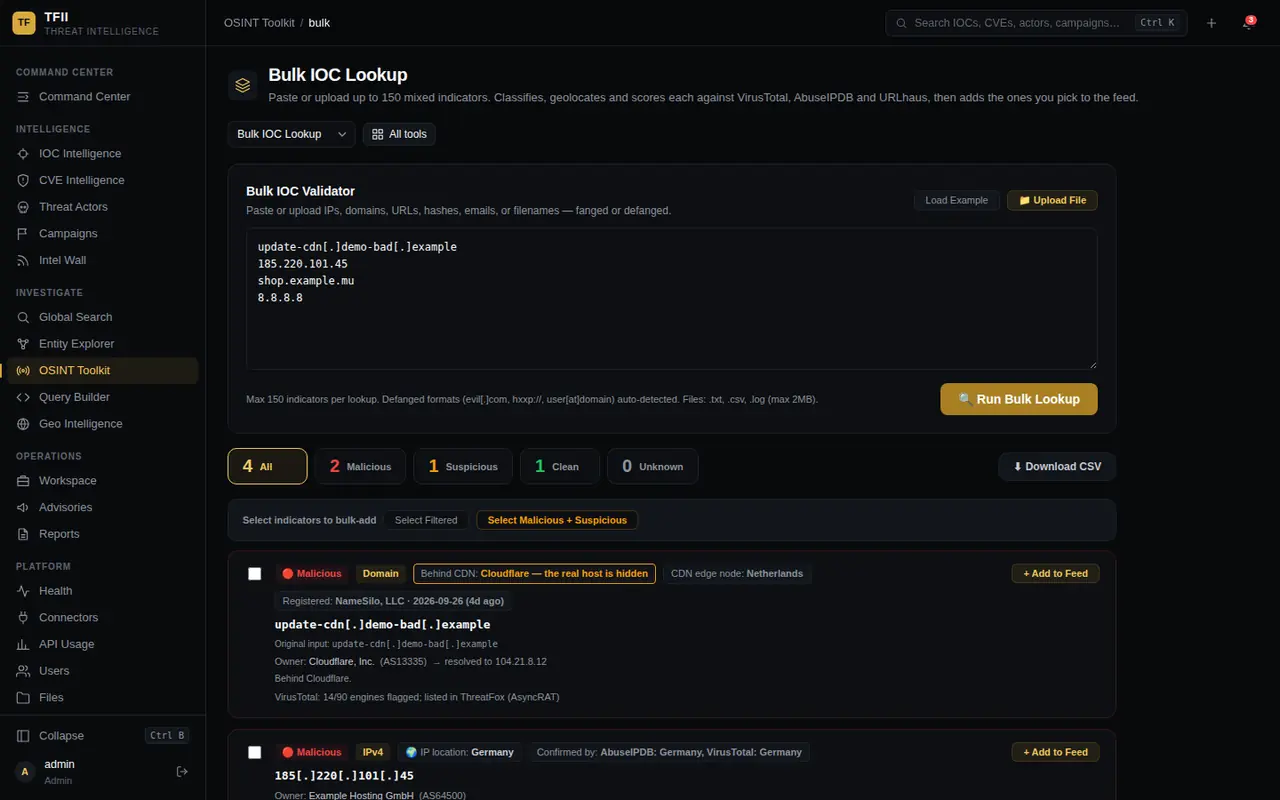
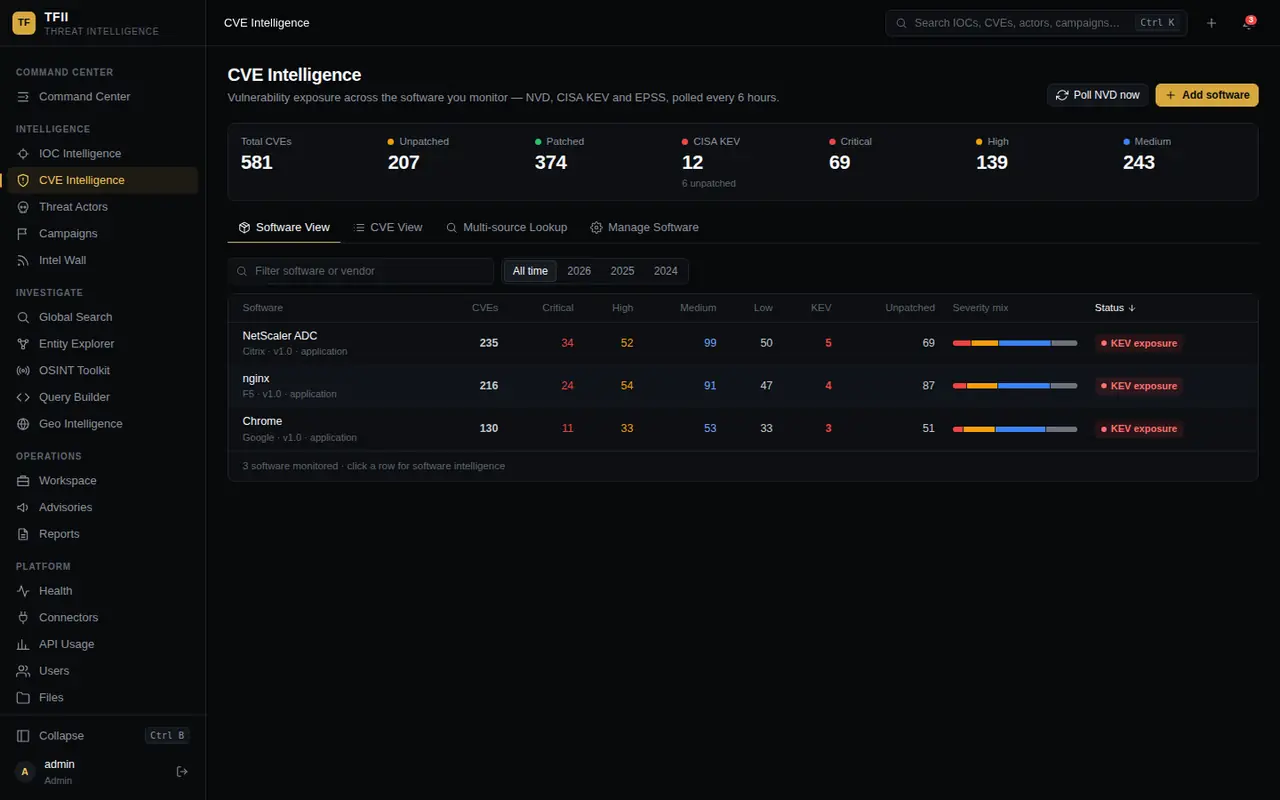
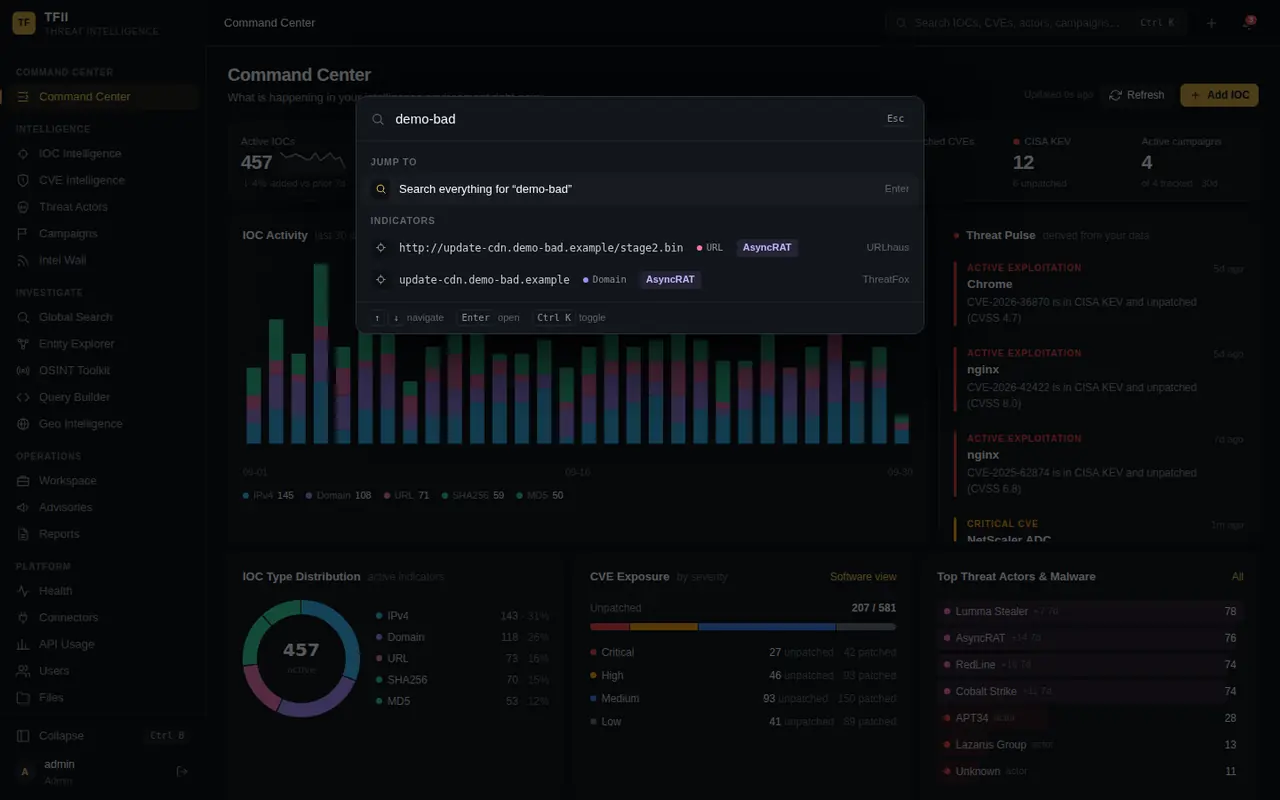
TFII shows its work on every indicator

A threat-intel platform where confidence isn't one opaque score from one feed.

TFIIPython · FastAPISTIX / TAXII
  • Independent sources are corroborated — and an aggregator is never double-counted
  • Locations are labelled for what they are: IP location, CDN edge, TLD registry, registrant country
  • Every indicator page spells out the reasoning behind its confidence
View TFII
Principle 02

Fail loudly, never silently

A control that quietly stops working is worse than one that was never there. Failure should be visible, specific and actionable.

The testWhat happens when this breaks at 3 a.m.?
IN PRACTICE
Where I've done it

From Kestrel's engine to Sentinel's connectors

In Kestrel every action declares what to do when it can't run — skip, queue, degrade or fail — and says so plainly. At work, the same habit keeps monitoring honest.

KestrelConnector healthLog Analytics
  • Kestrel surfaces blocked steps as clear, actionable states instead of silent no-ops
  • Validating connector health, ingestion status and data quality across client environments
  • So “no alerts” never quietly means “no data”
View Kestrel
Principle 03

Tune for signal, not volume

More data isn't more security. The goal is the smallest pipeline that still catches what matters.

The testDoes this alert earn its place in the queue?
IN PRACTICE
Where I've done it

30–40% less ingestion, same detection coverage

Filtering low-value events and tuning connectors across multiple client tenants at Ansen Technologies.

Microsoft SentinelKQLWorkbooks
  • Monthly log ingestion down 30–40% without impacting detection coverage
  • KQL analytics rules and hunting queries tuned to raise alert fidelity and cut false positives
  • A weekly Sentinel workbook that tracks ingestion volume and cost by source
View the workbook
Principle 04

Test the claims

If something says it works, something should fail when it stops being true — code and documentation alike.

The testWould a test fail if the explanation were wrong?
IN PRACTICE
Where I've done it

CertPrep's 534 tests — including the teaching copy

An exam-prep platform where the content is held to the same standard as the code.

CertPrepVitestNext.js
  • Where the lab shows an explanation beside a worked example, a test asserts the engine really agrees with it
  • Spotted a 93% answer-position bias in the question bank — then randomised and enforced a fix
  • Content validation runs alongside the unit tests
View CertPrep
Principle 05

Write it down so others can run it

A system only one person understands is a liability. Handover quality is part of the engineering.

The testCould someone else run this without me?
IN PRACTICE
Where I've done it

Runbooks, playbooks and a team lab

Documentation as a deliverable, not an afterthought.

RunbooksPlaybooksSplunk lab
  • Authored SOC engineering documentation, detection playbooks, onboarding procedures and runbooks to standardise deployments
  • Built a shared Splunk lab so L1/L2 analysts can practise outside production
  • A full government SOC delivered with zero post-deployment rework
Principle 06

Private by default

Collect only what's needed, keep it where it's yours, and make the safe path the default one.

The testDoes this data need to leave the device at all?
IN PRACTICE
Where I've done it

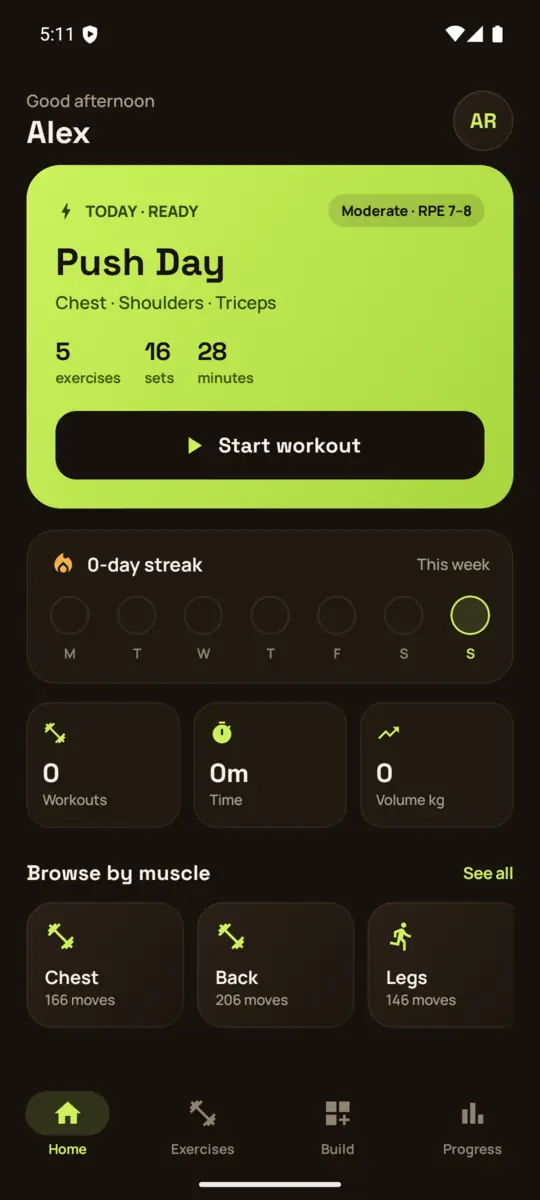
GetFit, Ledger and TFII keep your data yours

Privacy shows up as defaults, not settings.

GetFitLedgerTFII
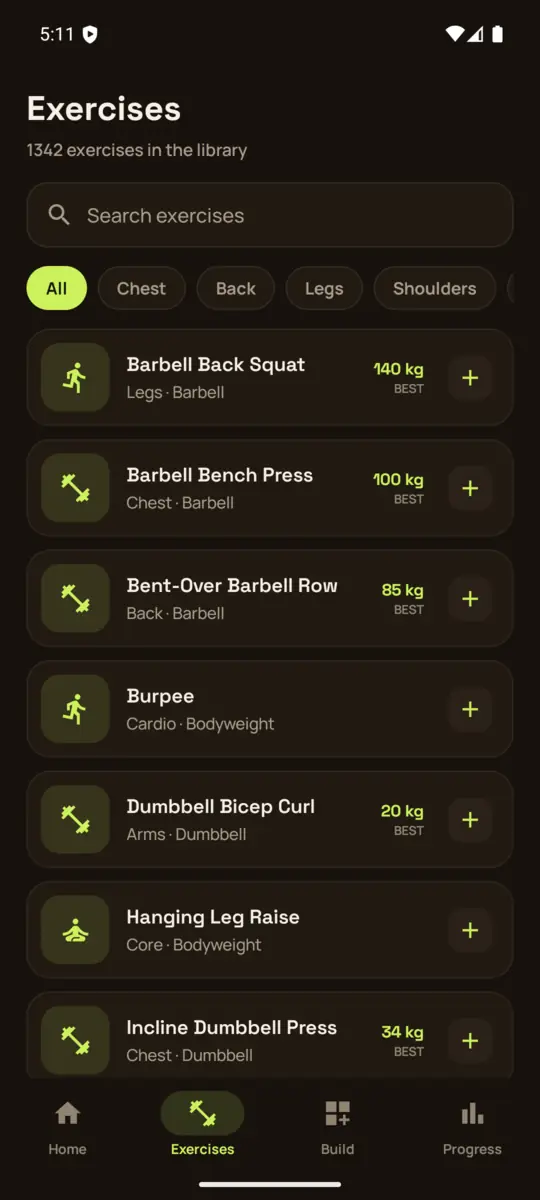
  • GetFit: no account, no analytics, no cloud sync — and Android backup switched off
  • Ledger: offline-first by design, with no cloud dependency
  • TFII: no telemetry, and each user's API keys are encrypted at rest and visible only to them
View GetFit
Pulled straight from my own repos and my day job — every claim has something real behind it.
04 — Projects

Things I've built.

Security tooling, training platforms and Android apps — all open on GitHub.

Detection & SIEM labs

Hands-on environments I build to learn each platform properly — and to give my team somewhere to practise.

LAB 01

Splunk SIEM Engineering

Shared training environment for L1/L2 analysts — Windows, Linux syslog and firewall ingestion, brute-force and suspicious-process detections, dashboards and saved searches.

LAB 02

IBM QRadar

QRadar Community Edition fed via Syslog/LEEF and WinCollect, with correlation rules for brute force, port scanning and suspicious authentication.

LAB 03

Wazuh + Defender + VirusTotal

Endpoint visibility and file-integrity monitoring, with custom detection rules enriched by VirusTotal for proactive malware triage.

LAB 04

ELK Stack

Full ingestion pipelines for system, firewall and web logs, real-time alerting for auth anomalies, and tuned Elasticsearch indexing and retention.

05 — Toolkit

The stack I work in.

SIEM & Detection

Microsoft SentinelSplunkWazuhIBM QRadarELK Stack

Endpoint & Identity

Defender XDRDefender for EndpointEntra ID · PIMIdentity ProtectionActive DirectoryPurview DLP

Cloud

Microsoft AzureAzure MonitorLog AnalyticsHuawei CloudCloudflare

Query & Detection

KQLSentinel AnalyticsSigma RulesSPL

Incident Response

NIST SP 800-61SANS PICERLMalware triageContainment playbooks

Threat Intelligence

IOC triageMITRE ATT&CK mappingMSRC Patch TuesdayCTI ingestion

Vulnerability Management

NessusQualysNexposeDefender Vuln. Mgmt

Penetration Testing

NmapMetasploitBurp SuiteOpenVASNiktoZAPWireshark

OS & Networking

Linux (Ubuntu, CentOS)Windows ServerVPNDNSSyslog · CEF · LEEF
06 — Certifications

Credentials, earned and in flight.

SC-200Earned

Microsoft Security Operations Analyst Associate

Sentinel, Defender XDR and KQL-driven threat response.

SY0-701Earned

CompTIA Security+

Core security concepts, operations and governance.

SC-900Earned

Microsoft Security, Compliance and Identity Fundamentals

Foundations across the Microsoft security portfolio.

CPTEarned

Certified Penetration Tester

Ehackify — hands-on offensive security methodology.

SC-500In progress

Microsoft Azure Security Engineer

Securing Azure workloads, networks and identities.

SC-401In progress

Microsoft Information Security Administrator Associate

Data protection, Purview DLP and information governance.

07 — Beyond the SOC

Open source & education.

Android · AOSP

Neoteric OS

A minimal custom Android ROM focused on UI/UX and performance, with a touch of security and privacy. I work at the AOSP level — device bring-up, vendor and hardware layers and framework forks across Xiaomi, Nothing and Qualcomm devices.

AOSPDevice treesSELinux policyQualcomm HALs
Neoteric-OS on GitHub
2019 — 2023

B.Tech, Computer Science & Engineering

KMEA Engineering College, Kochi
APJ Abdul Kalam Technological University (KTU), Kerala

08 — Contact

Let's build a SOC that sees more.

Hiring for a SOC or detection engineering role, or just want to compare notes on Sentinel and KQL? My inbox is open.

Connect on LinkedIn